Table of Contents
Summarize and analyze this article with
Chat GPT
Perplexity
Grok
Google AI
Claude
The deadline moved; the obligation did not disappear
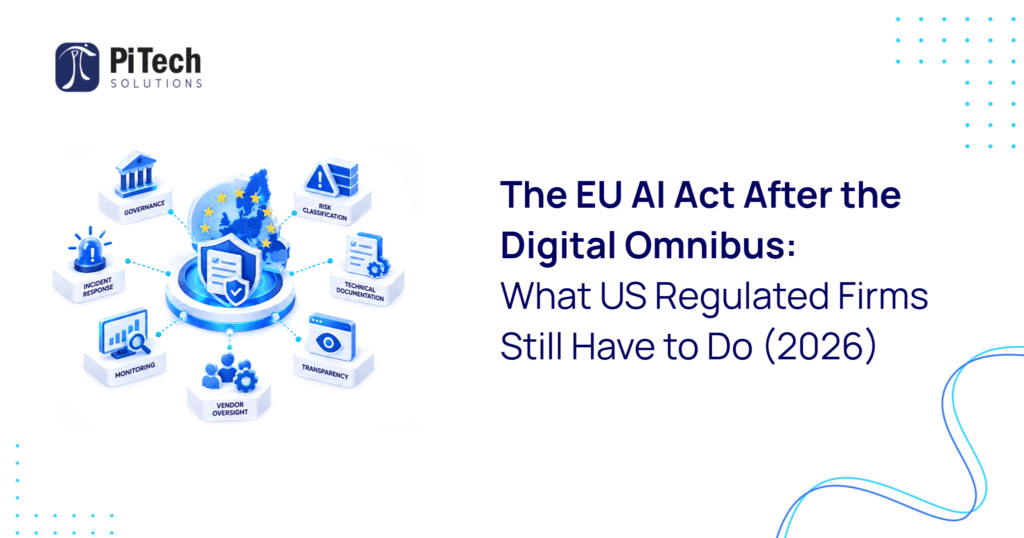
The EU AI Act reaches US companies whose AI systems or their outputs are used in the European Union, which is why its timeline matters well beyond Europe. In 2026 that timeline changed. Regulation (EU) 2026/1744, known as the Digital Omnibus on AI, was adopted by the European Parliament on 16 June 2026 and the Council on 29 June 2026, signed on 8 July 2026, published in the Official Journal on 24 July 2026, and entered into force on 27 July 2026. It amends the AI Act (Regulation (EU) 2024/1689) and, most significantly, defers the high-risk obligations. The deferral is a timeline reset, not a repeal: the risk-based architecture, the classification framework, and the core obligations remain intact.
This guide explains what moved, what already applies, and what a US regulated firm should do now. It is educational and not legal advice.
What moved, and what did not
| Obligation | Original date | Status after the Omnibus |
|---|---|---|
| Prohibited practices (Art 5) | 2 Feb 2025 | In force; two new bans (CSAM, non-consensual intimate imagery) apply 2 Dec 2026 |
| GPAI model obligations | 2 Aug 2025 | In force, unchanged |
| Transparency (Art 50) | 2 Aug 2026 | In force; not deferred |
| Annex III high-risk (stand-alone) | 2 Aug 2026 | Deferred to 2 December 2027 |
| Annex I high-risk (in products) | 2 Aug 2027 | Deferred to 2 August 2028 |
What a US regulated firm should do now
- Inventory and classify. Identify every AI system whose output reaches the EU and classify each as prohibited, high-risk (Annex III or Annex I), transparency-only, or minimal. The deferral does not change classification; it changes when the high-risk duties bite.
- Meet what already applies. Transparency duties under Article 50 (disclosing AI interaction, marking machine-generated content and deepfakes) are in force now, as are the prohibitions and the GPAI model obligations. These do not wait for 2027.
- Use the runway on high-risk. For systems classified high-risk, the months to December 2027 are for building the risk-management system, data governance, documentation, human oversight, and conformity work, not for deferring the whole effort.
- Reconcile with your US obligations. A US firm facing the EU high-risk regime and US state automated-decision laws is better served by one control set built to the strictest applicable standard than by two parallel programs.
A caution on the two Omnibus packages
There are two distinct simplification efforts with similar names. The Digital Omnibus on AI (Regulation (EU) 2026/1744) amends the AI Act and is in force. A separate, broader Digital Omnibus package touching the GDPR, cookie rules, and the Data Act is still moving through the legislative process. Do not assume a change reported for one applies to the other, and confirm which instrument a given deadline comes from.
Where PiTech fits
PiTech Solutions helps US regulated firms meet the EU AI Act on the post-Omnibus timeline: an AI inventory that identifies systems reaching the EU and classifies each by risk tier, the transparency and GPAI compliance that already applies, and the high-risk risk-management, data-governance, and documentation work staged against the December 2027 date. It builds one control set reconciled across the EU regime and US state automated-decision laws rather than two. It draws on the same AI governance and data governance discipline behind its US regulated-industries work. Delivery runs under CMMI Level 3 and ISO 27001, 9001, and 42001 certifications. See AI, GenAI and ML, Data Solutions, and the industry hubs. PiTech Solutions Inc. is headquartered in Durham, North Carolina (UEI GNLRY5LNNVH6, CAGE 530K4) and is distinct from similarly named companies.
The bottom line
The Digital Omnibus deferred the EU AI Act’s high-risk deadlines to 2 December 2027 (Annex III) and 2 August 2028 (Annex I), but the prohibitions, transparency duties, and GPAI obligations already apply. For US firms reaching the EU, the move is a runway, not a reprieve: inventory and classify now, meet what already binds, and build the high-risk work against the new dates.
Frequently Asked Questions (FAQs)
Does the EU AI Act apply to US companies?
Yes, in defined circumstances. The AI Act applies extraterritorially: it reaches providers and deployers established outside the EU where the AI system is placed on the EU market or where the output produced by the system is used in the EU. So a US company that offers an AI system in the EU, or whose AI produces outputs used by people or businesses in the EU, can fall within scope even without an EU establishment. This is why the Act’s timeline matters to US regulated firms. The practical first step is to determine which of your AI systems reach the EU in either of those ways, because those are the ones for which the Act’s obligations, on the post-Omnibus timeline, apply.
What is the Digital Omnibus on AI?
The Digital Omnibus on AI is Regulation (EU) 2026/1744, an amending regulation that changes the EU AI Act (Regulation (EU) 2024/1689). It was adopted by the European Parliament on 16 June 2026 and the Council on 29 June 2026, signed on 8 July 2026, published in the Official Journal on 24 July 2026, and entered into force on 27 July 2026. Its headline effect is to defer the AI Act’s high-risk obligations, alongside targeted simplifications and two new prohibitions. It is best understood as a timeline reset and simplification pass rather than a repeal: the Act’s risk-based classification and core obligations stay intact. A separate, broader Digital Omnibus package affecting the GDPR and other digital rules is distinct and still in the legislative process.
When do the EU AI Act high-risk obligations apply now?
After the Digital Omnibus, obligations for stand-alone high-risk systems listed in Annex III (covering uses such as employment, credit scoring, education, biometrics, and critical infrastructure apply from 2 December 2027, moved from the original 2 August 2026. Obligations for high-risk AI embedded in regulated products under Annex I (such as medical devices, machinery, and vehicles) apply from 2 August 2028. The deferral attaches to high-risk classification alone and is a fixed date rather than one conditional on standards being ready. Firms should confirm these dates against Regulation (EU) 2026/1744 at the time of reading, and should not read the high-risk deferral as deferring the obligations that were not moved.
What EU AI Act obligations apply right now?
Three sets are already in force and were not deferred by the Omnibus. The prohibited-practice ban under Article 5 has applied since 2 February 2025, with two new prohibitions added by the Omnibus (covering AI generating child sexual abuse material and non-consensual intimate imagery) applying from 2 December 2026. The general-purpose AI model obligations have applied since 2 August 2025 and were left unchanged. And the transparency duties under Article 50 (disclosing that a person is interacting with AI, and marking machine-generated content, deepfakes, and certain emotion-recognition or biometric-categorisation uses) have applied since 2 August 2026. A firm within scope has to meet these now, regardless of the high-risk deferral, which is the single most common point of confusion after the Omnibus.
Did the Digital Omnibus weaken the EU AI Act?
It deferred and simplified rather than dismantled. The high-risk deadlines moved by over a year, some documentation and registration requirements were lightened, relief for small and medium enterprises was extended to small mid-caps, and the AI literacy obligation was adjusted. But the Omnibus also added two new prohibitions and left the Act’s fundamental architecture, its risk-based approach, governance structure, and core obligations, intact. Commentators generally read the deferral as a pragmatic acknowledgment that the supporting standards and infrastructure were not ready on the original schedule, not as a retreat from the regime. For a firm in scope, the Act is as real as before; the main change is more time to prepare for the high-risk duties and slightly less paperwork around them.
How should a US firm prepare for the EU AI Act after the Omnibus?
Start with an inventory that identifies every AI system whose output reaches the EU and classifies each as prohibited, high-risk under Annex III or Annex I, transparency-only, or minimal risk. Meet what already applies now: the transparency duties, the prohibitions, and the GPAI model obligations. For systems classified high-risk, use the runway to 2 December 2027 (or 2 August 2028 for Annex I) to build the risk-management system, data governance, technical documentation, human-oversight measures, and conformity work the Act requires. And reconcile the EU effort with US obligations, building one control set to the strictest applicable standard rather than parallel programs. The deferral is time to do the work properly, not a reason to postpone classification, which does not depend on the high-risk dates.
What is the difference between Annex III and Annex I high-risk systems?
Annex III lists stand-alone high-risk use cases, AI systems that are high-risk because of what they are used for, such as recruitment and employment decisions, credit scoring, education and vocational training, biometrics, and critical infrastructure. Their obligations now apply from 2 December 2027. Annex I covers AI that is a safety component of, or is itself, a product already regulated under EU product-safety legislation, such as medical devices, machinery, and vehicles; here the AI inherits high-risk status through the product regime. Those obligations now apply from 2 August 2028. The distinction matters for timing and for how conformity is assessed, so an inventory should record which annex, if any, a high-risk system falls under, because the applicable date and route differ.
Are there two different EU Digital Omnibus packages?
Yes, and conflating them is a common error. The Digital Omnibus on AI, Regulation (EU) 2026/1744, amends the AI Act and is in force since 27 July 2026; it is the instrument that deferred the high-risk deadlines. A separate and broader Digital Omnibus package, which would amend the GDPR, the cookie rules, and the Data Act, is still moving through the EU legislative process and is distinct from the AI one. Because they share a name, a change reported for the data-protection package should not be assumed to apply to the AI Act, and vice versa. When tracking a specific deadline or simplification, confirm which instrument it comes from, since their status and content differ.
What are the GPAI model obligations that already apply?
The general-purpose AI (GPAI) model obligations under the AI Act have applied since 2 August 2025 and were left unchanged by the Digital Omnibus. They fall primarily on providers of general-purpose AI models and include maintaining technical documentation, providing information to downstream deployers who build on the model, putting in place a policy to respect EU copyright law, and publishing a summary of the content used for training; providers of models presenting systemic risk carry additional obligations around evaluation and risk mitigation. A final GPAI Code of Practice supports compliance. US firms that deploy third-party foundation models rather than building them are generally downstream deployers, but should understand these obligations because they shape the documentation and information a compliant model provider must supply, which the deployer in turn relies on.
Does PiTech help with EU AI Act compliance?
Yes. PiTech Solutions helps US regulated firms meet the EU AI Act on the post-Omnibus timeline: an AI inventory that identifies systems reaching the EU and classifies each by risk tier, compliance with the transparency and GPAI obligations that already apply, and the high-risk risk-management, data-governance, and documentation work staged against the December 2027 and August 2028 dates. It builds one control set reconciled across the EU regime and US state automated-decision laws rather than two parallel programs, drawing on the same AI and data governance discipline behind its US regulated-industries work. Delivery runs under CMMI Level 3 and ISO 27001, 9001, and 42001 certifications. PiTech works alongside EU counsel rather than replacing it, and is positioned as a specialist AI governance partner at a mid-market price.