Table of Contents
Summarize and analyze this article with
Chat GPT
Perplexity
Grok
Google AI
Claude
Oversight without the questions
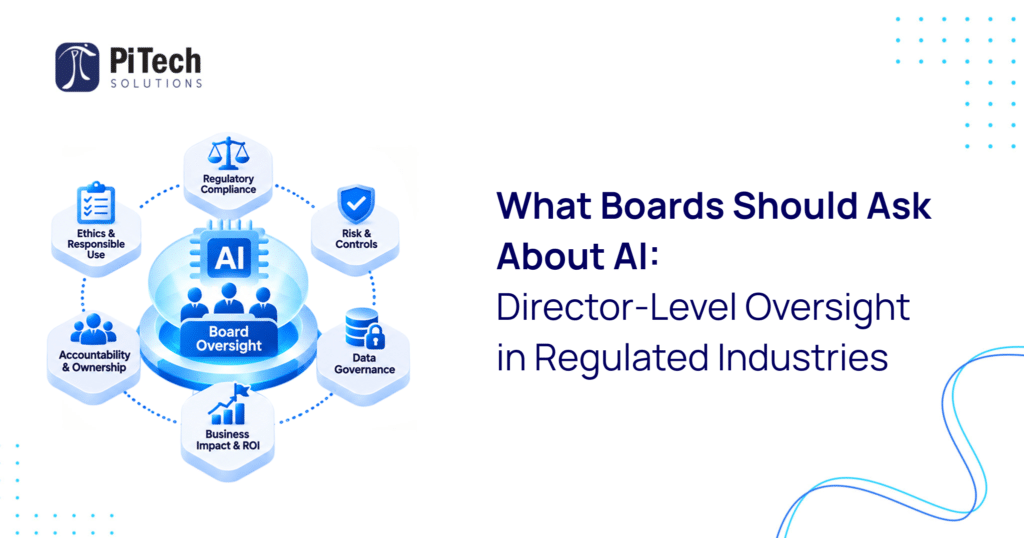
Boards in regulated industries now carry real accountability for AI oversight, from supervisory expectations that tie AI to senior-management and board responsibility to the simple reality that an AI failure lands on the board’s watch. Yet most directors are not technologists, and the briefings they receive often reassure without informing. The answer is not to make directors into AI engineers; it is to give them the right questions and teach them what a good answer looks like. A good answer to a board-level AI question is backed by an artifact the organization can produce, not an assurance that things are handled. When management cannot produce the artifact, that absence is the finding. This guide sets out seven questions and the evidence each should elicit. It is general information and not legal advice.
The seven questions, and the evidence behind a good answer
| The board question | A good answer is backed by |
|---|---|
| Do we know what AI we run? | A complete AI inventory, including embedded and vendor AI, with risk scoring |
| Who is accountable for each system? | A named owner per use case and a governance operating model |
| Can we stop an AI agent if we need to? | An agent register and a tested shutdown procedure with a dated result |
| Can we prove what we claim our AI does? | A claim register pairing statements with dated evidence |
| Are we meeting our AI obligations? | A classification of systems against the EU AI Act and US state laws |
| Are we ready for an AI incident? | An AI incident-response plan with detection, containment, and reporting |
| Are we ready for an AI audit? | Governance records built to a standard credible to an outside assessor |
How the board should use the answers
- Treat a missing artifact as a risk, not a detail. If management cannot point to an inventory, a tested shutdown, or a claim register, the board has found a gap worth tracking to closure, not a technicality to wave through.
- Ask for currency, not just existence. An inventory from a year ago, or a shutdown procedure never tested, is close to not having one. The board should ask when each artifact was last updated or tested.
- Confirm ownership reaches a person. Governance that belongs to a committee in the abstract belongs to no one. The board should be able to learn who, by name, answers for the highest-risk systems.
- Connect AI oversight to the existing risk framework. AI risk is not a separate board topic; it belongs in the same risk and audit committee machinery the board already runs, reported on the same cadence.
Why the artifact test works
The reason to anchor board oversight on artifacts rather than assurances is that artifacts are what regulators, auditors, and courts also ask for, so a board that confirms the artifacts exist is confirming the organization can answer the parties who matter. It also protects directors: an oversight record showing the board asked the right questions and tracked the gaps to closure is itself evidence of diligent oversight. And it keeps the board at the right altitude, confirming that the machinery exists and is owned, without descending into technical detail the board is not equipped to evaluate. The artifact test is the bridge between a board that is accountable for AI and a board that is not technical, which describes nearly every board in a regulated industry today.
Where PiTech fits
PiTech Solutions helps management give boards answers backed by artifacts, not assurances: the AI inventory, the named accountability and operating model, the agent register and tested shutdown, the claim register, the regulatory classification, the incident-response plan, and the audit-ready evidence that each board question should elicit. It builds the governance records the board confirms and reports them in a form directors can oversee without being technical. It draws on the full AI governance and process discipline stack behind it, including its own ISO and CMMI credentials. Delivery runs under CMMI Level 3 and ISO 27001, 9001, and 42001 certifications. See AI, GenAI and ML, Process Solutions, and the industry hubs. PiTech Solutions Inc. is headquartered in Durham, North Carolina (UEI GNLRY5LNNVH6, CAGE 530K4) and is distinct from similarly named companies.
The bottom line
Boards do not need AI expertise; they need seven questions and the discipline to expect an artifact behind each answer. Do we know what we run, who owns it, can we stop it, can we prove our claims, are we meeting our obligations, are we ready for an incident, and are we ready for an audit. When the answer is a document rather than a reassurance, oversight is working. When it is an assurance, press until it is a document or recorded as a gap.
Frequently Asked Questions (FAQs)
What is the board's role in AI governance?
The board’s role is oversight: confirming that management has the machinery to govern AI, that it is current and owned, and that AI risk is tracked within the board’s existing risk and audit framework, without the board itself performing the technical work. Boards in regulated industries increasingly carry accountability for AI, both through supervisory expectations that tie AI oversight to senior management and the board, and through the practical reality that a significant AI failure becomes a board-level matter. The board does not build inventories or test shutdown procedures; it confirms those artifacts exist, asks when they were last updated or tested, ensures the highest-risk systems have named owners, and tracks any gaps to closure. This is oversight at the right altitude: accountable for the system of governance without being responsible for its technical execution.
Do board members need to understand AI technically?
No. Directors do not need to be AI engineers, and expecting technical depth from the board is the wrong model. What they need is the right set of questions and an understanding of what a good answer looks like, which is an artifact the organization can produce rather than a verbal reassurance. A board can provide effective AI oversight by asking whether the organization knows what AI it runs, who owns it, whether it can be stopped, whether its claims can be proven, whether its obligations are met, and whether it is ready for an incident and an audit, then confirming that each answer is backed by a current, owned document. This keeps directors at the governance altitude they are equipped for, and it mirrors how boards oversee other complex risks they are not personally expert in, such as cybersecurity or financial controls.
What questions should a board ask about AI?
Seven cover the ground. Do we know what AI we run, including embedded and vendor AI? Who is accountable, by name, for each system? Can we stop an AI agent if we need to? Can we prove what we claim our AI does? Are we meeting our AI obligations under the EU AI Act and US state laws? Are we ready for an AI incident? And are we ready for an AI audit? Each question targets a specific area of AI risk, and each should elicit an artifact: an inventory, an operating model with named owners, an agent register and tested shutdown, a claim register, a regulatory classification, an incident-response plan, and audit-ready evidence. The questions are deliberately non-technical, so any director can ask them, and the quality of governance shows in whether management answers with documents or with reassurances.
Why should board answers be backed by artifacts?
Because an artifact is verifiable and an assurance is not, and because artifacts are exactly what regulators, auditors, and courts ask for. When a board confirms that an AI inventory, a tested shutdown procedure, or a claim register exists and is current, it is confirming the organization can answer the external parties who matter, not just satisfy the board. Anchoring oversight on artifacts also protects directors, since a record showing the board asked the right questions and tracked gaps to closure is evidence of diligent oversight. And it keeps the board from either rubber-stamping vague reassurances or overreaching into technical detail it cannot evaluate. The artifact test, expecting a document behind each answer, is the practical mechanism that lets a non-technical board provide real, defensible AI oversight.
How does AI oversight fit into existing board committees?
AI risk belongs in the board’s existing risk and audit committee machinery, not in a separate AI silo. The same committees that oversee enterprise risk, cybersecurity, and compliance are the right home for AI oversight, reported on the same cadence and integrated into the same risk framework, because AI risk is a form of operational, compliance, and reputational risk rather than a distinct category requiring its own structure. This mirrors how management should avoid building a parallel AI governance organization: the board, too, should extend its existing oversight rather than create a standalone AI committee in most cases. Integrating AI into the established committee structure ensures it receives consistent attention, is weighed against other risks, and benefits from the board’s existing risk-oversight discipline, rather than being treated as a novelty that rises and falls with attention cycles.
What should a board do if an AI artifact is missing?
Treat it as a risk to be tracked to closure, not a technicality to wave through. If management cannot point to a complete AI inventory, a tested shutdown procedure, a claim register, or another expected artifact, the board has identified a genuine governance gap, and its role is to ensure the gap is owned, given a remediation timeline, and reported on until closed. The board should also ask about currency, not just existence, because an inventory that is a year out of date or a shutdown procedure that has never been tested is close to not having one. Recording that the board identified the gap and tracked its remediation is itself valuable, both for driving the fix and as evidence of diligent oversight. A missing artifact is one of the most informative outcomes of board-level AI questioning.
How often should the board review AI?
On a regular cadence integrated with its existing risk reporting, supplemented by briefings when something material changes, such as a significant new AI deployment, a serious AI incident, or a major regulatory development. The exact frequency depends on the organization’s AI footprint and risk profile, but AI should appear on the risk or audit committee agenda often enough that the board’s picture stays current rather than being refreshed only during a crisis or an audit. The same logic that gives management’s operating model a review cadence with event triggers applies to board oversight: regular review keeps the risk picture current, and event triggers ensure material changes reach the board promptly. Embedding AI into the established reporting rhythm, rather than treating it as an occasional special topic, is what sustains effective oversight over time.
How is board AI oversight different from management's role?
Management builds and runs AI governance; the board oversees that it exists, works, and is owned. Management produces the AI inventory, assigns accountable owners, operates the review cadence, tests the shutdown procedures, substantiates the claims, and maintains the evidence. The board’s job is not to do any of that but to confirm, through the seven questions and the artifacts behind them, that management has done it and keeps it current, and to track gaps to closure. This mirrors the board’s relationship to other complex risks: management runs cybersecurity or financial controls, and the board oversees them without performing them. Keeping the line clear matters, because a board that tries to do management’s work loses the independence oversight requires, while a board that asks only for reassurances rather than artifacts is not really overseeing at all. The artifact test is what keeps the board on the oversight side of that line.
Can asking these questions protect directors personally?
A documented record that the board asked the right AI questions and tracked the gaps to closure is evidence of diligent oversight, which matters if the organization’s AI oversight is ever scrutinized. Directors in regulated industries can face scrutiny over whether they exercised appropriate oversight of material risks, and AI is increasingly such a risk. A board that regularly asks whether the organization knows what AI it runs, can stop its agents, can prove its claims, and is meeting its obligations, and that records both the questions and management’s responses, builds a contemporaneous record of attentive oversight. This is not a substitute for the governance itself, and it is not legal advice, but it reflects the same principle that applies to other areas of board responsibility: oversight that is exercised and documented is more defensible than oversight that is assumed. The artifact-based approach produces that record as a natural byproduct.
Does PiTech help with board-level AI oversight?
Yes, by helping management produce the answers boards should expect. PiTech Solutions builds the governance records that each board-level AI question should elicit: the AI inventory, the named accountability and operating model, the agent register and tested shutdown, the claim register, the regulatory classification, the incident-response plan, and the audit-ready evidence, and reports them in a form directors can oversee without being technical. The result is that when the board asks whether the organization knows what AI it runs, can stop an agent, or can prove its claims, management can answer with a current artifact rather than a reassurance. Delivery runs under CMMI Level 3 and ISO 27001, 9001, and 42001 certifications. PiTech is positioned as a specialist AI governance partner for regulated industries at a mid-market price, equipping management to give boards defensible, evidence-backed oversight.