Table of Contents
Summarize and analyze this article with
Chat GPT
Perplexity
Grok
Google AI
Claude
Independence is becoming a defined term
For most of the AI governance era, assurance was a posture: an organization asserted that its AI was fair, accurate, and controlled. That is changing. Independence is becoming a defined function, with structure and, increasingly, registration behind it. California’s Governor signed Senate Bill 813 and Assembly Bill 1405 on 9 September 2026, creating a designation route for independent verification organizations and a state registry for AI auditors, with the operative criteria and registry arriving in 2028 and 2029. Neither binds a private party today, but together they signal that an AI audit market is forming and that independent evidence, not self-assertion, is what will satisfy regulators, customers, and courts. The organizations ready for that shift are the ones building audit-ready records now.
This guide explains what AI assurance is and how to be ready for it. It is educational and not legal advice.
What an AI audit examines
| Area | What an assessor looks for | The record it relies on |
|---|---|---|
| Inventory completeness | Every AI system, including embedded and vendor AI, is accounted for | A complete AI inventory with risk scoring |
| Claim substantiation | Public statements about the AI are backed by evidence | A claim register with dated artifacts |
| Decision accountability | Consequential automated decisions are governed and explainable | A decision register and human-review records |
| Testing and fairness | The AI was tested for accuracy and disparate impact | Documented, dated test results |
| Controls and monitoring | Governance controls exist and operate, not just on paper | Tested controls with owners and dates |
| Independence | Evidence was produced or reviewed outside the build team | Attributable, independent assessment records |
Assurance rests on records you may already be building
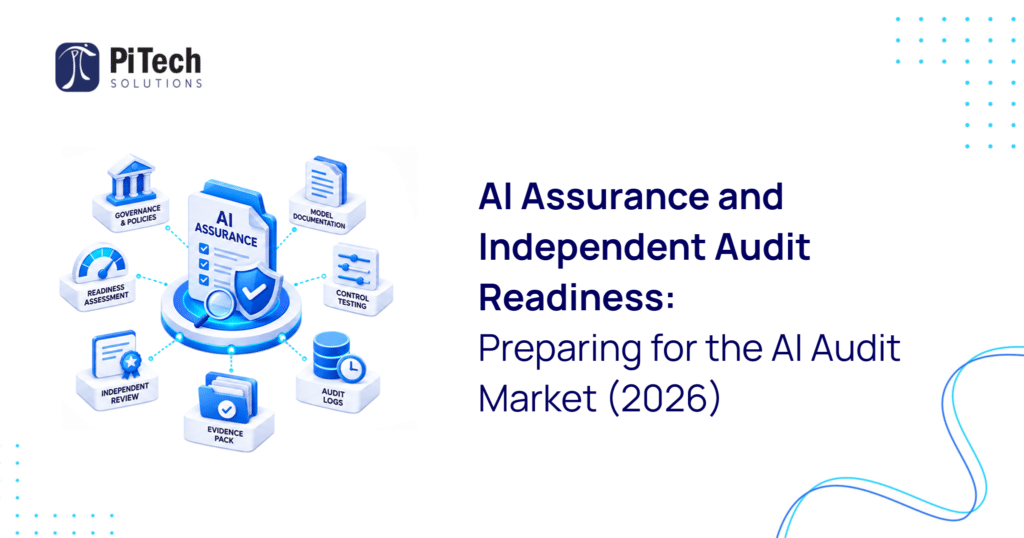
The useful insight is that AI assurance does not require a separate body of work. An AI audit examines the same records good AI governance already produces: the inventory that shows what AI the organization runs and how it is risk-scored, the claim register that pairs statements with evidence, the decision register that records consequential automated decisions, the test results that show accuracy and fairness, and the tested controls that show governance operates. What an audit adds is the requirement that this evidence be credible to an outsider, which means it has to be dated, attributable, and, for the highest-consequence systems, produced or reviewed by someone outside the team that built the system. An organization that has built its governance records to that standard is audit-ready; one that built them only for internal use will need to strengthen their independence and evidentiary quality.
Designing for independence now
The cheapest time to build independence into AI evidence is before an audit requires it. For any AI system whose output informs a customer decision, a clinical decision, or a price, arrange for the validating evidence to be produced or reviewed by a party outside the build team, and record who did it. As designation routes and auditor registries come into effect, that independence will increasingly need to meet defined criteria, and organizations that already separate evidence from the builder will adapt far more easily than those retrofitting it under deadline. Building for independence now also improves the governance itself, because evidence that can withstand outside scrutiny is simply better evidence.
Where PiTech fits
PiTech Solutions helps regulated organizations become AI-audit-ready: a complete AI inventory, a claim register of substantiated statements, a decision register of governed automated decisions, dated testing for accuracy and fairness, and tested controls, all built to a standard that holds up when someone outside the organization reads them, with independence designed in for the highest-consequence systems. It prepares organizations for the emerging AI audit market rather than scrambling when an audit is requested. It draws on the full AI governance and data governance stack behind it. Delivery runs under CMMI Level 3 and ISO 27001, 9001, and 42001 certifications. See AI, GenAI and ML, Data Solutions, and the industry hubs. PiTech Solutions Inc. is headquartered in Durham, North Carolina (UEI GNLRY5LNNVH6, CAGE 530K4) and is distinct from similarly named companies.
The bottom line
AI assurance is becoming a defined, independent function, with auditor registries forming and buyers asking for third-party evidence. An AI audit examines the records good governance already produces: inventory, claim register, decision register, testing, and controls. Build those to a standard credible to an outsider, with independence designed in for high-consequence systems, and you will pass an AI audit rather than assemble one under pressure.
Frequently Asked Questions (FAQs)
What is AI assurance?
AI assurance is the independent evaluation of whether an AI system does what its owner claims it does, and whether it operates safely, fairly, and in compliance, producing evidence that a third party can rely on. It goes beyond an organization’s own assertion that its AI is sound by having that soundness examined and evidenced in a way that is credible to outsiders, regulators, customers, counterparties, or courts. AI assurance can range from internal independent review, where a party inside the organization but outside the build team evaluates a system, to external audit by a dedicated assurance provider. As the AI audit market forms, assurance is shifting from a self-declared posture toward a defined function with standards and, increasingly, registered auditors, which makes building audit-ready evidence a practical priority for regulated organizations.
What does an AI audit examine?
An AI audit typically examines whether the organization’s AI is fully inventoried (including embedded and vendor AI), whether public claims about the AI are substantiated by evidence, whether consequential automated decisions are governed and explainable, whether the AI was tested for accuracy and disparate impact, whether governance controls actually exist and operate rather than appearing only in policy, and whether the evidence was produced with appropriate independence from the build team. In other words, an audit tests the same things good AI governance produces, but to the standard that the evidence must be credible to an outsider: dated, attributable, and independently produced or reviewed for the highest-consequence systems. The specific scope depends on the assurance framework and the regime, but these areas are the common core of what an AI assessor looks for.
What are California's AI auditor laws (SB 813 and AB 1405)?
On 9 September 2026, California’s Governor signed Senate Bill 813 and Assembly Bill 1405, which together begin to formalize independent AI assurance. SB 813 creates a designation route for independent verification organizations through a state agency, and AB 1405 establishes a state registry for AI auditors. Neither binds a private party today, and the operative criteria and registry mechanisms are set to arrive in 2028 and 2029, with the laws’ agency-facing duties taking effect on 1 January 2027. Their significance is directional: they indicate that independence in AI evaluation is becoming a defined, registered function rather than a self-declared posture. Organizations should treat them as a signal that building independent, audit-grade AI evidence now is cheaper than retrofitting it when such frameworks become operative. Confirm the laws’ status and timelines against the enacted text at publish.
Why is an AI audit market emerging now?
Because AI has moved into consequential, regulated use faster than self-assurance can satisfy the parties who rely on it. Regulators increasingly expect evidence rather than assertion, buyers and counterparties ask for independent validation before trusting an AI system, and emerging laws are beginning to define and register AI auditors. At the same time, high-profile AI failures have made third-party scrutiny more attractive to boards and customers. The combination, regulatory pressure, buyer demand, legal formalization, and reputational risk, is creating demand for independent AI evaluation, which is the AI audit market. For organizations deploying AI, this means the ability to produce credible, independent evidence is becoming a competitive and compliance necessity, not just a governance nicety, and the ones ready for audits will have an advantage.
How is AI assurance different from internal AI governance?
Internal AI governance is what an organization does to manage its own AI: building inventories, registers, testing, and controls. AI assurance is the independent evaluation of that governance and the AI it governs, producing evidence credible to outsiders. The two are complementary: good internal governance produces the records an audit examines, and assurance tests whether those records are complete, accurate, and independently credible. The key difference is the standard of evidence. Governance records built only for internal use may be sufficient to run the program but not to satisfy an external assessor who requires dated, attributable, and independently produced evidence. Assurance readiness therefore means building governance records to that higher evidentiary standard from the start, so that the same records serve both internal management and external audit.
What records make an organization AI-audit-ready?
The same records good AI governance produces, built to a standard credible to an outsider: a complete AI inventory that accounts for every system including embedded and vendor AI, with risk scoring; a claim register that pairs each public statement about the AI with a dated evidence artifact; a decision register that records consequential automated decisions and the human review around them; documented, dated testing for accuracy and disparate impact; and tested governance controls with named owners. What makes these audit-ready, as opposed to merely functional, is that the evidence is dated, attributable, and, for high-consequence systems, produced or reviewed independently of the build team. An organization that maintains these records to that standard can respond to an AI audit with existing evidence rather than assembling it under deadline, which is both faster and more credible.
Why does independence matter in AI assurance?
Because evidence produced solely by the team that built a system invites the criticism that it was not objectively tested, and an audit exists precisely to provide objective assurance. For any AI whose output informs a customer decision, a clinical decision, or a price, having the validating evidence produced or reviewed by a party outside the build team makes it credible to a regulator, auditor, or counterparty in a way that self-produced evidence is not. Emerging laws reinforce this by creating designation routes for independent verification organizations and registries for AI auditors, which will define what independence means in practice. Building independence into AI evidence now, by separating evidence from the builder for high-consequence systems, is cheaper than retrofitting it and produces better evidence regardless of whether a formal audit ever occurs.
How should an organization prepare for an AI audit?
Start by assessing the AI governance records it already has against the standard an outside assessor would apply: is the inventory complete, are claims substantiated with dated artifacts, are consequential decisions governed and explainable, is there dated testing for accuracy and fairness, and do controls actually operate. Close the gaps that assessment reveals, strengthening evidence that was built only for internal use so it is dated, attributable, and defensible. For the highest-consequence systems, arrange for validating evidence to be produced or reviewed independently of the build team. And track the emerging assurance frameworks and auditor-registration regimes so the organization’s approach aligns with the criteria they define. Doing this proactively turns an eventual audit into a review of existing evidence rather than a scramble, and it improves the governance itself along the way.
Is AI assurance only relevant to large organizations?
No. Any organization whose AI makes or informs consequential decisions, about credit, coverage, employment, health, or pricing, faces the same pressure for independent evidence, regardless of size, because the parties asking for assurance (regulators, customers, counterparties) care about the consequence of the decision, not the size of the organization. Smaller organizations may face assurance demands through procurement, when a larger customer requires independent evidence before trusting their AI, or through regulation that applies by activity rather than size. The practical implication is that audit readiness is a function of what an organization’s AI does, not how big it is, and that building audit-grade governance records is worthwhile for any regulated deployer of consequential AI. The scope of the effort scales with the AI footprint, but the need for credible evidence does not disappear at smaller scale.
Does PiTech help with AI audit readiness?
Yes. PiTech Solutions helps regulated organizations become AI-audit-ready: a complete AI inventory, a claim register of substantiated statements, a decision register of governed automated decisions, dated testing for accuracy and fairness, and tested controls, all built to a standard that holds up when someone outside the organization reads them, with independence designed in for the highest-consequence systems. It prepares organizations for the emerging AI audit market, including the independent-verification and auditor-registry frameworks taking shape, rather than scrambling when an audit is requested. Delivery runs under CMMI Level 3 and ISO 27001, 9001, and 42001 certifications. PiTech is positioned as a specialist AI-governance and assurance-readiness partner for regulated industries at a mid-market price, and can act as the independent reviewer for evidence produced by internal build teams.